Friday, October 30, 2026 · Cyber news, in panels.
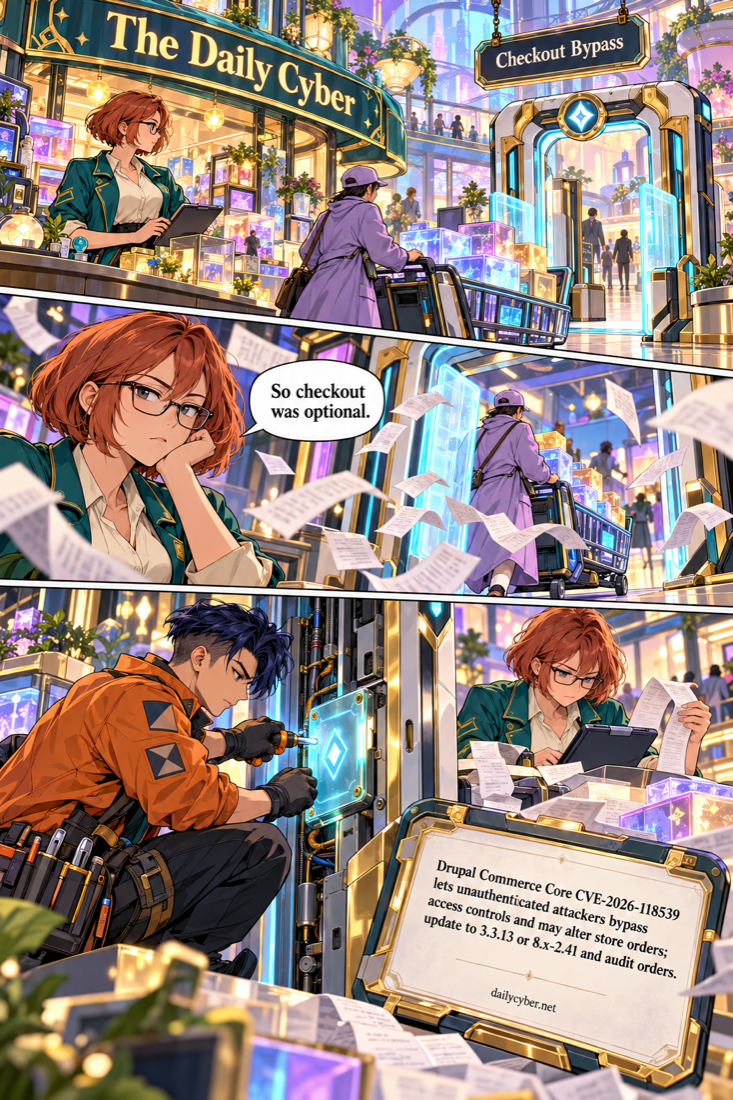
Drupal says attackers are exploiting CVE-2026-118539, an authorization bypass in Commerce Core that may let unauthenticated users alter store orders. Upgrade to 3.3.13 or 8.x-2.41 and audit orders for inconsistencies.

Drupal Checkout Bypass Under Active Exploitation

Drupal says attackers are exploiting CVE-2026-118539, an authorization bypass in Commerce Core that may let unauthenticated users alter store orders. Upgrade to 3.3.13 or 8.x-2.41 and audit orders for inconsistencies.

Get tomorrow's comic in your inbox

One panel a day. No spam, unsubscribe with one click.